Intrusion detection system in VANET using NetSim
| Applicable Versions | NetSim Standard | NetSim Pro |
| Applicable Release | V13.1 |
TABLE OF CONTENTS
- Introduction
- Infographic
- Files used in this project
- Steps to simulate
- Network Settings
- Results and Discussion
Introduction
VANET refers to the group of vehicles that are interlinked to one another through a wireless network. Along with technology, comes the threats. Like other wireless networks, VANETs also are vulnerable to various security threats. one small security breach can cause big damage in the case of VANETs as in this case human lives are involved. Intrusion Detection Systems (IDS) are employed in VANETs to detect and identify any malicious activity in the network. The IDS works by analyzing the network and detecting any intrusions tried or made in the network so that proper steps could be taken timely to prevent damage from such activities.
Infographic
Files used in this project
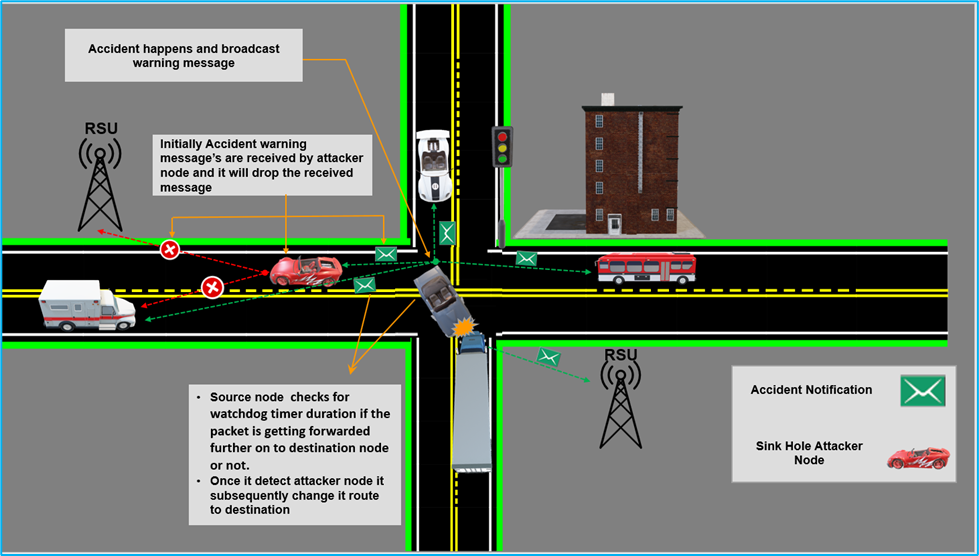
The following steps show how a user can run the IDS in NetSim to detect a malicious node and then set up a new route to the destination to avoid the malicious node.
- Creating Malicious nodes for a particular network scenario is explained in the Malicious.c file.
- To detect the intruder and to send data via a new route, the following files are added in DSR and IEEE802_11
Pathrater.c
This file contains code for avoiding the malicious node and finding a new route (once the IDS detects the malicious node) in networks running DSR in Layer 3. Note that this system would work only for UDP and not for TCP since TCP involves receiving acks from the destination.
If _NETSIM_PATHRATER_ is defined, the code is used to validate routes. When the Node is a Malicious Node, and a Route Reply is processed, the Function verifies the route reply in the route cache and checks for the blacklisted node. i.e., malicious node. When a malicious node is found that route entry is deleted from the cache.
Watchdog.c
This file contains code for the IDS and is added in IEEE802_11 operating in Layer 2.
If _NETSIM_WATCHDOG_ is defined, a watchdog timer starts the moment a packet is sent. Once a packet is forwarded to the next-hop node, the current node checks for watchdog timer duration if the packet is getting forwarded further on to the destination node or not.
The malicious node does not forward packets that it receives. The watchdog timer in the node (which forwarded the packet to the malicious node) expires. A counter is present which measures the number of times the watchdog timer expires (in other words the number of packets sent out but not forwarded by the next-hop node). Once this counter’s value reaches the failure threshold the next hope is marked by the current node as a malicious node.
Steps to simulate
- Download the IDS_VANET project using the below link
- https://github.com/NetSim-TETCOS/IDS_for_VANETs/archive/refs/heads/main.zip
- Follow the instructions specified in the following link to download and set up the Project in NetSim: Downloading and setting up NetSim File Exchange Projects
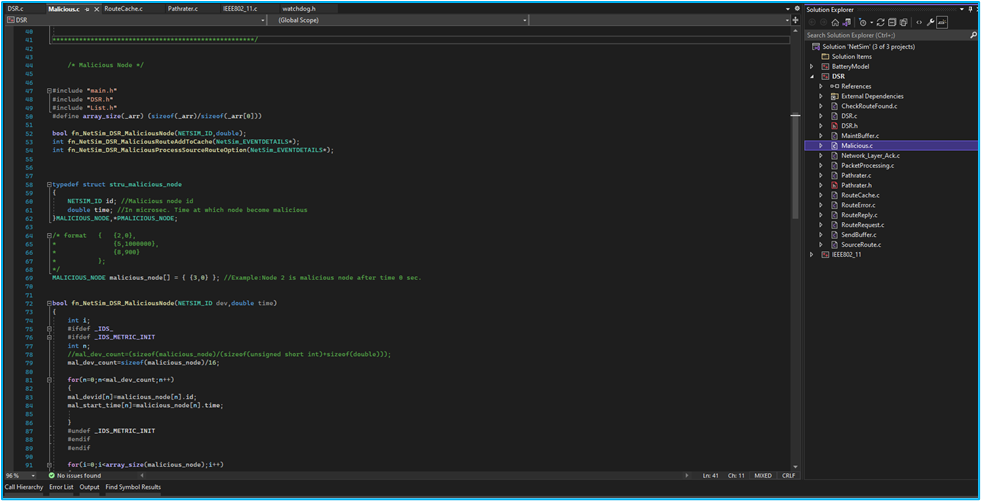
- Open the Source codes in Visual Studio by going to Your work-> Source code and Clicking on the Open code button in the NetSim Home Screen window.
- A malicious.c file is added to the DSR source code project in which is the malicious node and its behavior are defined.
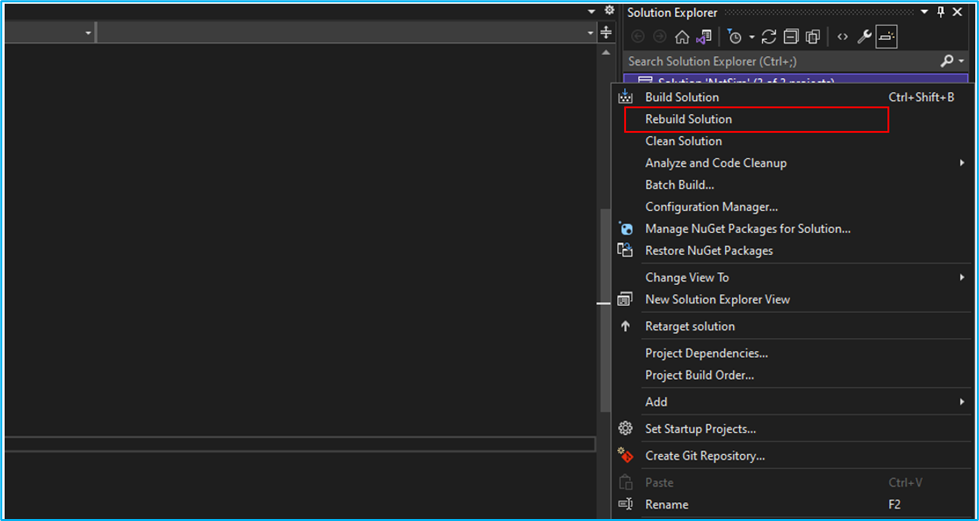
- Now right-click on Solution explorer in the solution explorer and select Rebuild.
- Upon successful build modified libIEEE802_11.dll and libDSR.dll file gets automatically updated in the directory containing NetSim binaries.
NetSim Scenario

Network Settings
- The downloaded folder consists of a folder named SUMO;this folder contains a file SumoRun.py a python script.This file must be replaced with the original SumoRun.py file present in the bin folder of NetSim install directory(C:\ProgramFiles\NetSim\Standard_v13_1\bin)
- The IDS_VANET_Workspace comes with a sample network configuration that is already saved. To open this example, go to Your work on the home screen of NetSim and click on the IDS_VANET_Example from the list of experiments.
- Wireless Link Properties
- Channel Characteristics - Pathloss only
- Path loss model - LOG_DISTANCE
- Path loss exponent - 3.5
4. Application Properties
Application Properties | |
| Application type | CBR |
Source Id | 2 |
Destination Id | 1 |
Transport Protocol | UDP |
5. Enable Packet trace in NetSim GUI.
6. Run Simulation for 300 seconds.
Results and Discussion
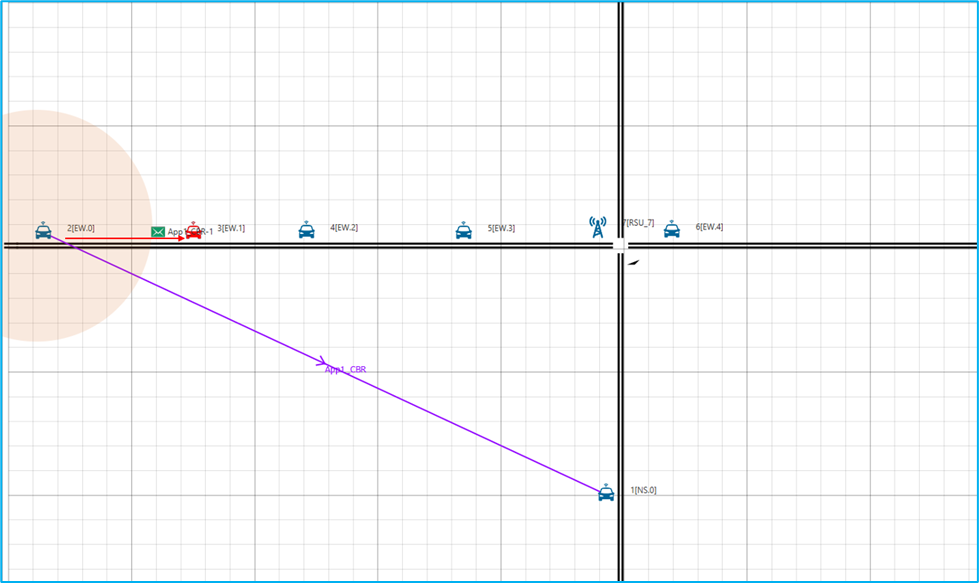
- Open animation window. The Initial flow of packets are till node 3 since node 3 is detected as malicious.
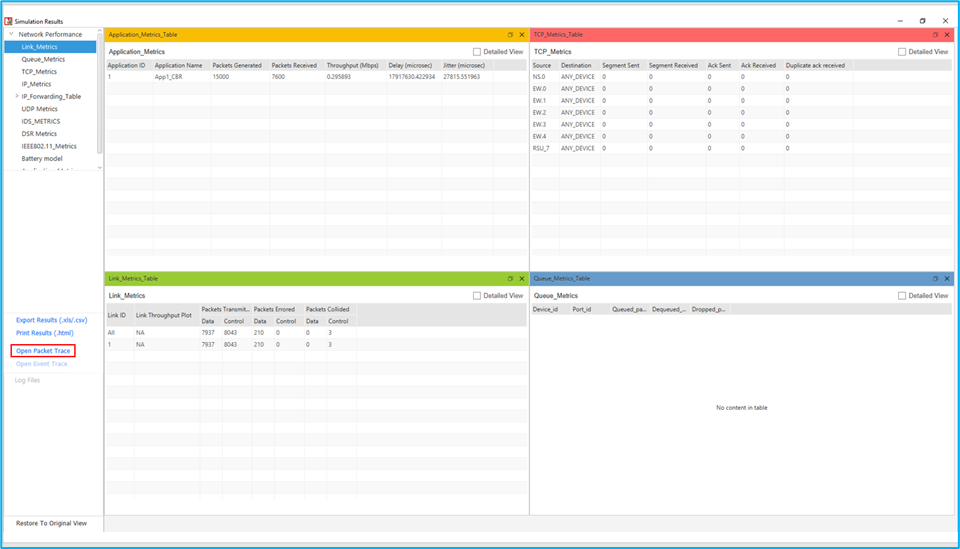
- In the Result Dashboard, open packet trace using open packet trace hyperlink
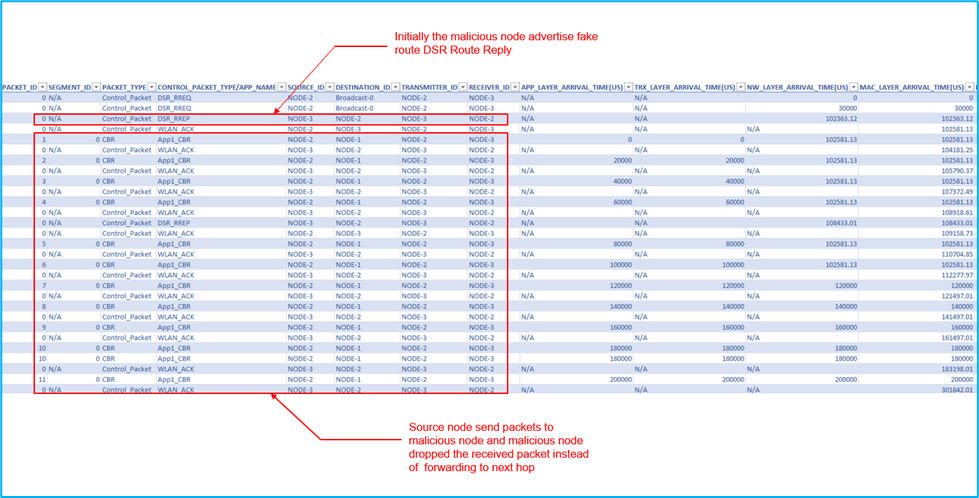
- Here you would notice initially the malicious node(node-3) sends fake route information to Source node(node-2).Source node send packets to malicious node and it will drop the received packets.
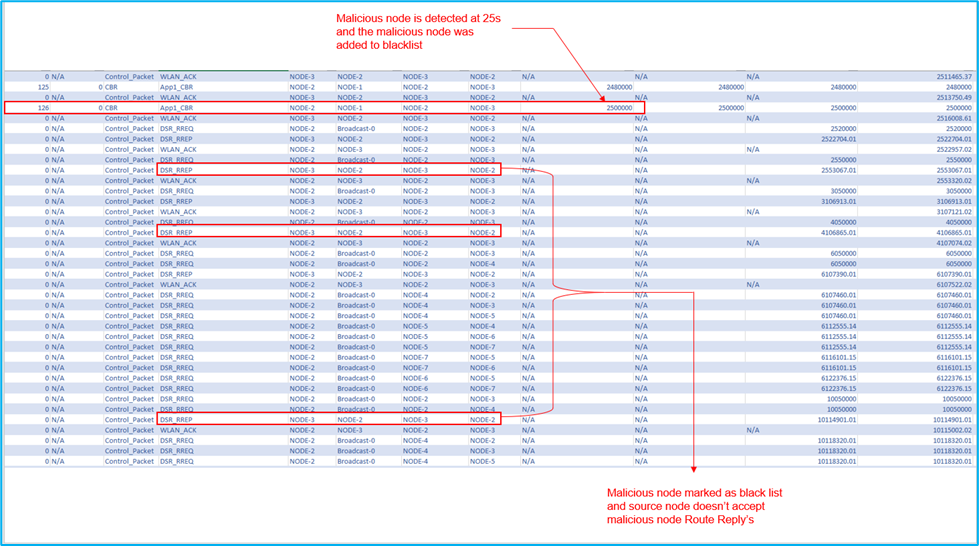
- As Per the original code setting the Watchdog timer is set to 2 seconds and the failure threshold is set to 20 packets. So, you would notice that around 25 seconds, the malicious node is detected and the route to destination would change in the subsequent route discovery process.
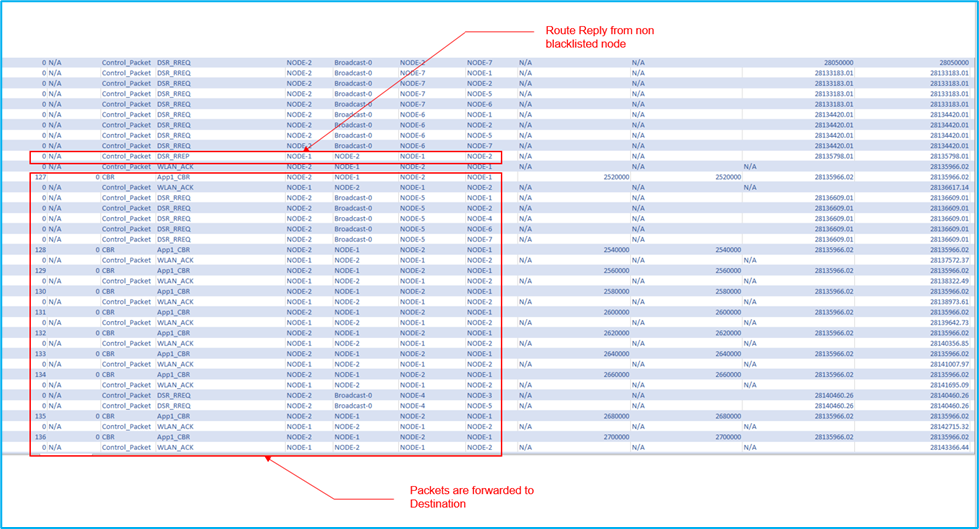
- Once the Source node receives DSR_RREP from the non-listed blacklist node then it will forward the packets to that node.
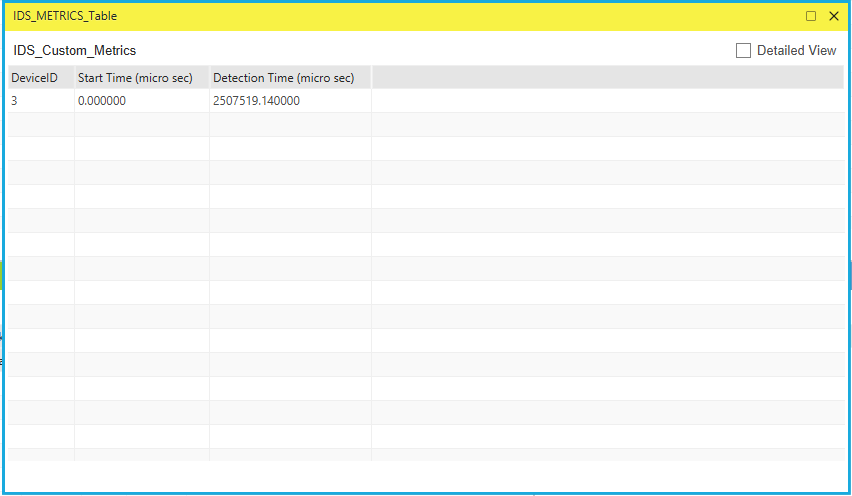
- The time at which a malicious node is detected can be obtained from the CUSTOM METRICS (IDS METRICS) in the results window where the
- start time - time from which a node becomes malicious,
- detection time - time at which the node was added to blacklist can be obtained.
Useful webpages
1. NetSim documentation: https://tetcos.com/netsim-documentation.html
2. NetSim VANETs overview: https://tetcos.com/vanets.html